The most important quantum story today is not another qubit milestone. It is the widening gap between organizations that are beginning to change cryptographic infrastructure now and those still treating quantum risk as something to revisit later.
The conversation around quantum risk is becoming much more practical.
On X, the loudest discussion is still coming from crypto and blockchain communities. Bitcoin’s exposed public keys, post-quantum wallet designs, new blockchain architectures, and projects claiming to be “quantum ready” are driving much of the attention.
Some of that activity is marketing. Some of it is speculative. But underneath it is a legitimate architectural question that applies far beyond cryptocurrency:
How difficult will it be to replace the cryptography your organization depends on?
That is where the conversation becomes much more important.
Post-quantum migration is not simply an algorithm swap. Organizations have certificates, identities, APIs, software signatures, embedded devices, long-lived data, third-party platforms and vendor dependencies built around existing cryptographic assumptions.
Once you see the problem that way, the arrival date of a cryptographically relevant quantum computer becomes only part of the equation.
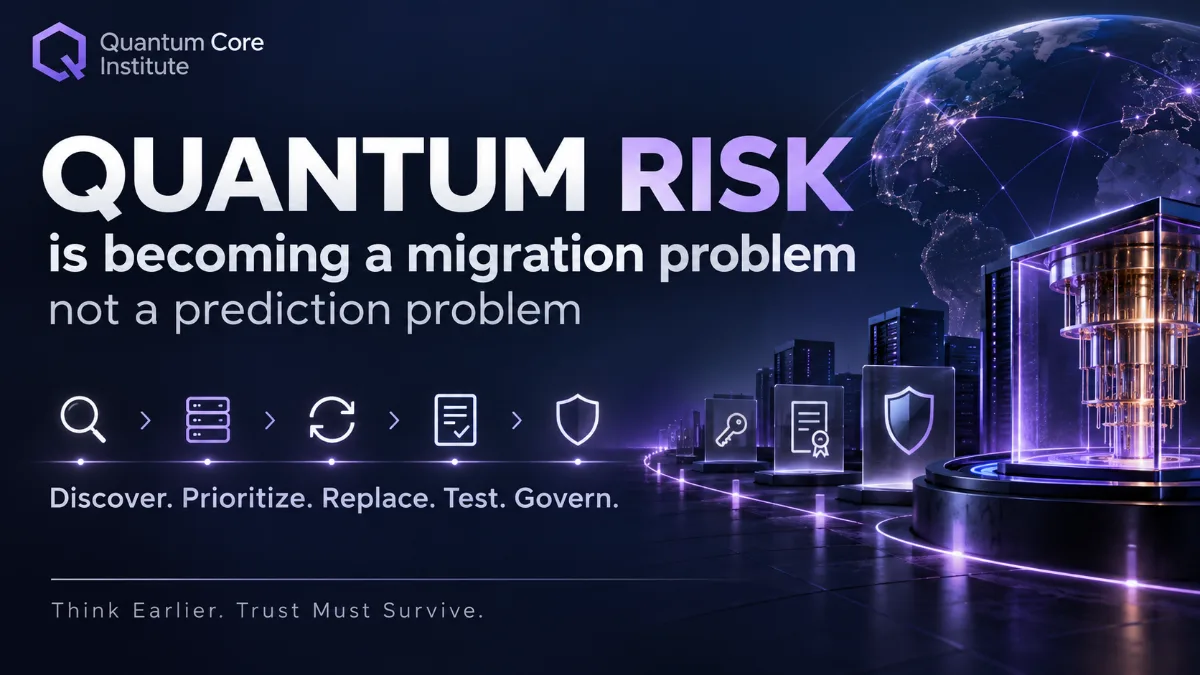
The other clock is already running. It is the amount of time required to discover, prioritize, replace, test and govern what you already have.