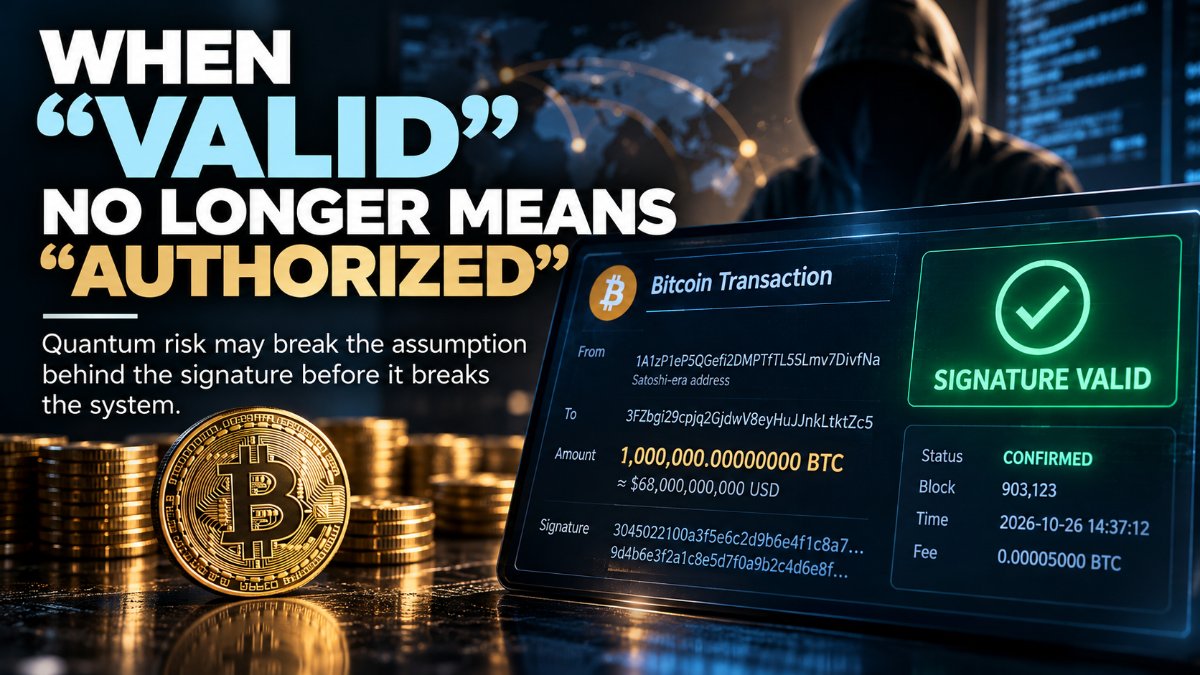
Bitcoin provides an unusually visible laboratory for this problem because public-key exposure can be measured directly on-chain. Glassnode estimated earlier this year that approximately 6.04 million BTC, or 30.2% of issued supply, sat in outputs where the public key was already visible. Other methodologies produce different estimates. A more recent ChainQuery analysis places the figure above 7 million BTC. The differences reflect classification and methodology, but the important point is consistent: a substantial quantity of Bitcoin already has public keys exposed on-chain.
That does not mean those coins can be stolen today. Current quantum computers are nowhere close to performing the required attack. Independent analyses explicitly make that distinction.
What it does mean is that public-key exposure is already an observable condition. The future question is what happens if the mathematical assumption protecting those keys stops holding.
Coinbase’s quantum advisory work has highlighted roughly 1.7 million BTC in legacy pay-to-public-key outputs alone, many associated with very early Bitcoin activity. It also points out that address reuse exposes millions more BTC belonging to active users and institutional wallets.
This is why the current discussion about emergency-response criteria is important.
A credible quantum incident would not necessarily arrive with a flashing banner saying: QUANTUM ATTACK DETECTED.
It might arrive as a perfectly valid cryptographic event whose legitimacy suddenly becomes uncertain. That is a very different security problem.
The second signal comes from crypto-agility efforts.
Starknet’s programmable-account model demonstrates one possible approach: separate account identity from a single immutable signature scheme so verification methods can change without forcing users to abandon the account itself. Other projects are exploring hash-based signatures, hybrid authorization, and post-quantum account layers.
Whether any particular project ultimately becomes the model is less important than the architectural principle: Cryptographic identity should be capable of surviving a change in cryptographic assumptions.
The third signal comes from enterprise infrastructure.
Cisco has now introduced quantum-resilient capabilities across parts of its networking portfolio, including new Wi-Fi 7 infrastructure, and has committed to quantum-safe communications capabilities across much of its core portfolio by the end of 2026. Its guidance explicitly frames harvest-now, decrypt-later as a present risk and emphasizes planned migration rather than waiting for a quantum breakthrough.
That may seem far removed from Bitcoin. It is not. Both situations confront the same underlying question: What happens when cryptographic proof remains technically valid but the trust assumption behind it has changed?