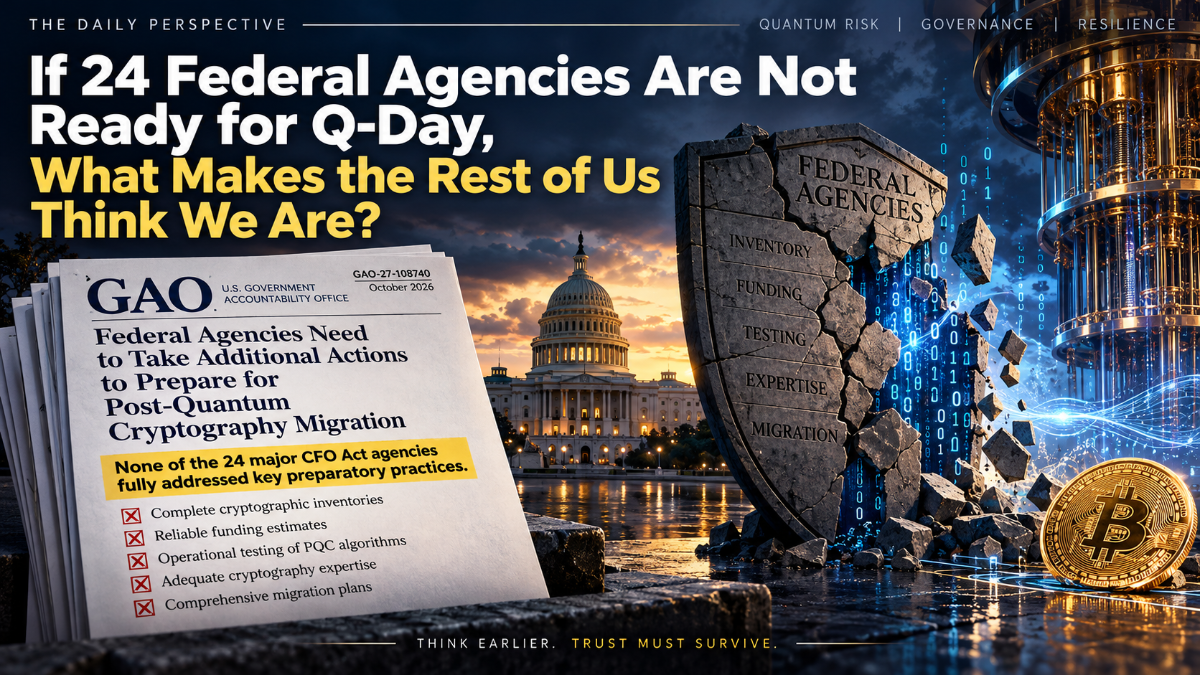
The GAO report may be one of the most useful quantum-readiness signals we have seen this year because it exposes a misconception. The hard part of post-quantum migration is not choosing the algorithm. NIST has already done much of that work.
The hard part is everything surrounding the algorithm. Finding where cryptography is used. Determining which implementations are vulnerable. Understanding what data must remain protected and for how long. Finding embedded cryptographic dependencies inside applications, devices, identities, certificates, APIs, firmware, cloud infrastructure, and vendor products. Determining which systems can support new algorithms. Testing them under real operational conditions. Budgeting the transition. Assigning accountability. Managing third parties. And proving that the organization is actually making progress.
That is why the GAO finding should matter far beyond Washington.
If a large federal agency does not have an accurate cryptographic inventory, it has a quantum-readiness problem.
If a bank does not have one, it has the same problem.
If a healthcare organization does not have one, same problem.
If a critical-infrastructure operator cannot identify which certificates, machine identities, firmware, and vendor systems depend on vulnerable public-key cryptography, it does not matter how many reports it has read about Q-Day.
It is not ready. That leads to a question every board should ask: “Can management show us the inventory, the priorities, the testing results, and the migration roadmap?”
Not the PowerPoint.
Not the quantum forecast.
Not the vendor brochure.
The evidence.
That is the threshold between awareness and readiness. The federal government is discovering just how wide that gap can be. Private organizations should learn from it before they have to discover the same thing the expensive way.
Think Earlier. Trust Must Survive.